Crack the Code of Cyber Security
Crack the Code of Cyber Security in an age where data has become the new oil, cybersecurity stands as the sentinel between you and digital catastrophe. Networks, apps, and personal devices are constantly under siege, often by threats that are nearly invisible. Yet for those who dare to crack cyber security code, there lies a thrilling realm of strategy, logic, and innovation. It’s not merely about defense—it’s about mastering the digital battlefield with finesse.
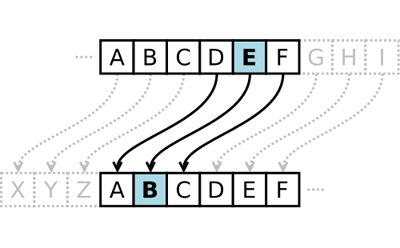
Understanding how to crack cyber security code doesn’t mean breaking in. Instead, it means breaking through complexity, demystifying jargon, and decoding the best practices that protect the integrity of modern systems. This article is your key to that realm—your map to navigate and triumph over the digital dangers.
The Cybersecurity Conundrum
At its core, cybersecurity is the practice of shielding systems, networks, and data from digital threats. But unlike traditional threats, these come silently. They slip past outdated firewalls, mimic trusted interfaces, or piggyback on third-party apps. They evolve faster than most industries can adapt.
That’s precisely why knowing how to crack cyber security code is indispensable. It requires more than technical know-how. You need an eye for anomalies, a mindset for continuous learning, and the tenacity to stay ahead of ever-morphing digital predators.
The Anatomy of a Cyber Attack
To defend, one must first comprehend the offensive playbook. Cyberattacks are no longer crude; they’re orchestrated with surgical precision. Here’s how they generally unfold:
- Reconnaissance – The attacker gathers intel, mapping vulnerabilities in systems and human behavior.
- Weaponization – A malicious payload is crafted. It could be ransomware, spyware, or a Trojan horse.
- Delivery – Through phishing emails, infected websites, or USB drops, the attack is deployed.
- Exploitation – Weaknesses in software or users are exploited.
- Installation – Malware anchors itself within the system, often undetected.
- Command and Control (C2) – The attacker gains remote access, steering the system like a ghost driver.
- Actions on Objectives – Data is exfiltrated, encrypted for ransom, or manipulated for disruption.
To truly crack cyber security code, each of these stages must be neutralized, ideally before exploitation.
Passwords: The First Frontier
Let’s begin with the most basic—and most abused—element: passwords. Too often, users fall into predictable patterns. “123456” and “qwerty” still rank among the most common passwords globally.
Advanced password cracking software can guess these in seconds. Instead, strong passwords should be long, complex, and random. Better yet, implement a password manager to generate and store them. Add multi-factor authentication (MFA), and you’ve erected an additional wall against infiltration.
When aiming to crack cyber security code, understanding human error is just as vital as understanding code.
Phishing: The Psychological Trap
Phishing exploits human emotions—urgency, curiosity, trust. These attacks mimic trusted entities, convincing users to click malicious links or surrender credentials. And now, with AI-generated emails and deepfake audio, phishing has reached uncanny levels of realism.
Mitigating phishing requires a culture of skepticism. Always verify unexpected communications. Avoid clicking on untrusted links. Hover over URLs. Contact organizations directly if something feels “off.” Cultivating a zero-trust mindset is fundamental when trying to crack cyber security code.
Firewalls and Antivirus: The Reactive Guardians
Think of firewalls as the gatekeepers. They control incoming and outgoing traffic based on predetermined rules. Antivirus software, meanwhile, detects and eliminates malicious code that slips through.
But reactive tools have limits. Advanced threats can bypass them using obfuscation and encryption. This is why modern security demands proactive defense.
Machine learning-based detection, behavioral analytics, and heuristic scanning now form the cutting edge. Knowing when to replace or augment traditional tools is essential when you want to crack cyber security code effectively.
Network Security: The Digital Moat
Your network is the bloodstream of digital operations. It connects devices, people, and servers. Therefore, it’s a prime target.
Securing a network includes:
- Segmenting systems to limit movement post-breach.
- Monitoring traffic in real-time using intrusion detection systems (IDS).
- Encrypting data in transit with VPNs and SSL certificates.
- Applying patches and firmware updates regularly.
A weak point in the network is an open invitation. When you learn to crack cyber security code, sealing these entry points becomes second nature.
Social Engineering: The Mind Games
Social engineering is the art of manipulating people into divulging confidential information. From tailgating into secure buildings to impersonating a technician, attackers exploit trust and social norms.
Defense against this is rooted in awareness. Security training should not be annual—it should be continuous. Everyone from interns to CEOs must be trained to spot manipulation.
And remember, security is communal. When everyone is vigilant, the entire organization benefits. That mindset is a big part of how to crack cyber security code.
Application Security: The Fortress Within
Applications—whether web, mobile, or desktop—are gateways to sensitive information. Bugs in code can be exploited to inject malicious scripts (like SQL injection or cross-site scripting).
Best practices here include:
- Code reviews and peer testing.
- Automated vulnerability scanning.
- Penetration testing to mimic real-world attacks.
- Secure DevOps (DevSecOps) integration.
A secure application environment doesn’t happen by accident. It’s architected with intention. Those seeking to crack cyber security code must learn to identify and eliminate risks from the inside out.
Insider Threats: The Enemy Within
Not all threats are external. Disgruntled employees, careless contractors, or uninformed partners can cause major damage.
Monitoring user behavior, enforcing access controls, and employing the principle of least privilege can mitigate this. It’s not about distrusting your team—it’s about safeguarding your ecosystem.
In complex organizations, this layer of protection is critical to truly crack cyber security code at a comprehensive level.
Cloud Security: Protecting Skyborne Assets
The shift to cloud computing has revolutionized business agility—but also introduced unique vulnerabilities. Misconfigured servers, insecure APIs, and data exposure are common issues.
Cloud security essentials include:
- Identity and Access Management (IAM).
- Data encryption at rest and in transit.
- Cloud-native security tools and logging.
- Compliance alignment (like ISO 27001 or SOC 2).
Knowing how to navigate cloud infrastructure and secure its many components is crucial when aiming to crack cyber security code.
Artificial Intelligence in Cybersecurity
AI has transformed defense strategies. Predictive analytics, anomaly detection, and autonomous responses are now integral.
AI can sift through terabytes of data to find needle-in-a-haystack threats in real time. It’s like having a thousand analysts working non-stop. But with great power comes new threats—AI itself can be weaponized.
Understanding both the offensive and defensive potential of AI is the next frontier for those who want to crack cyber security code with authority.
Incident Response: When the Worst Happens
No system is unbreachable. That’s why an effective incident response (IR) plan is paramount. It’s not just about responding—it’s about responding fast, smart, and with minimal damage.
A solid IR plan includes:
- Preparation – defining roles, tools, and contacts.
- Identification – detecting the breach quickly.
- Containment – isolating affected systems.
- Eradication – removing the threat entirely.
- Recovery – restoring operations.
- Post-incident review – learning and adapting.
This feedback loop is vital. Every breach should be a stepping stone toward a stronger system. That’s part of the DNA for anyone determined to crack cyber security code.
Cybersecurity Culture: Everyone’s Job
The strongest firewall can’t stop a careless click. Technology alone can’t protect an organization. People must be trained, policies must be enforced, and attitudes must shift.
Build a security-first culture by:
- Hosting regular training sessions.
- Rewarding cautious behavior.
- Making cybersecurity part of performance metrics.
True protection comes when cybersecurity becomes second nature. That’s when an organization has not just technology but a mindset that can crack cyber security code daily.
Future Trends to Watch
Cybersecurity is not static—it evolves as fast as threats emerge. Here’s what’s on the horizon:
- Quantum-resistant encryption to survive next-gen computation.
- Decentralized identity systems that give users full control.
- Zero Trust Architecture (ZTA) as a new standard.
- Privacy-enhancing computation to analyze data securely.
Being future-ready means always learning. For those committed to staying ahead, learning to crack cyber security code is a lifelong pursuit.
Final Thoughts
Cybersecurity isn’t just a profession. It’s a responsibility, a mindset, and in many ways, a modern superpower. In a landscape of invisible enemies, those who understand how to crack cyber security code become the unsung guardians of our digital age.
Whether you’re an aspiring analyst, a curious entrepreneur, or a tech-savvy student, now’s the time to immerse in the art and science of cybersecurity. Not just to protect systems—but to protect people, privacy, and the promise of a secure future.
Want an SEO meta description and subheading structure next?